

After reading, you can build a first inventory from sources you already have and keep it current without extra effort.
Definition
ISO/IEC 27001 Annex A control 5.9 calls for an inventory of information and other associated assets, including owners. CIS Controls 1 and 2, the first two of the 18, cover enterprise assets and software.
Why it matters
An unknown laptop never gets patched, and an unknown SaaS account stays open after someone leaves. Most other controls quietly assume the inventory exists.
It also pays off during an incident, when the first questions are which system is hit, who owns it and how critical it is.
How it works
Decide what to record: name, type, owner, location or provider, classification, criticality and date of last review.
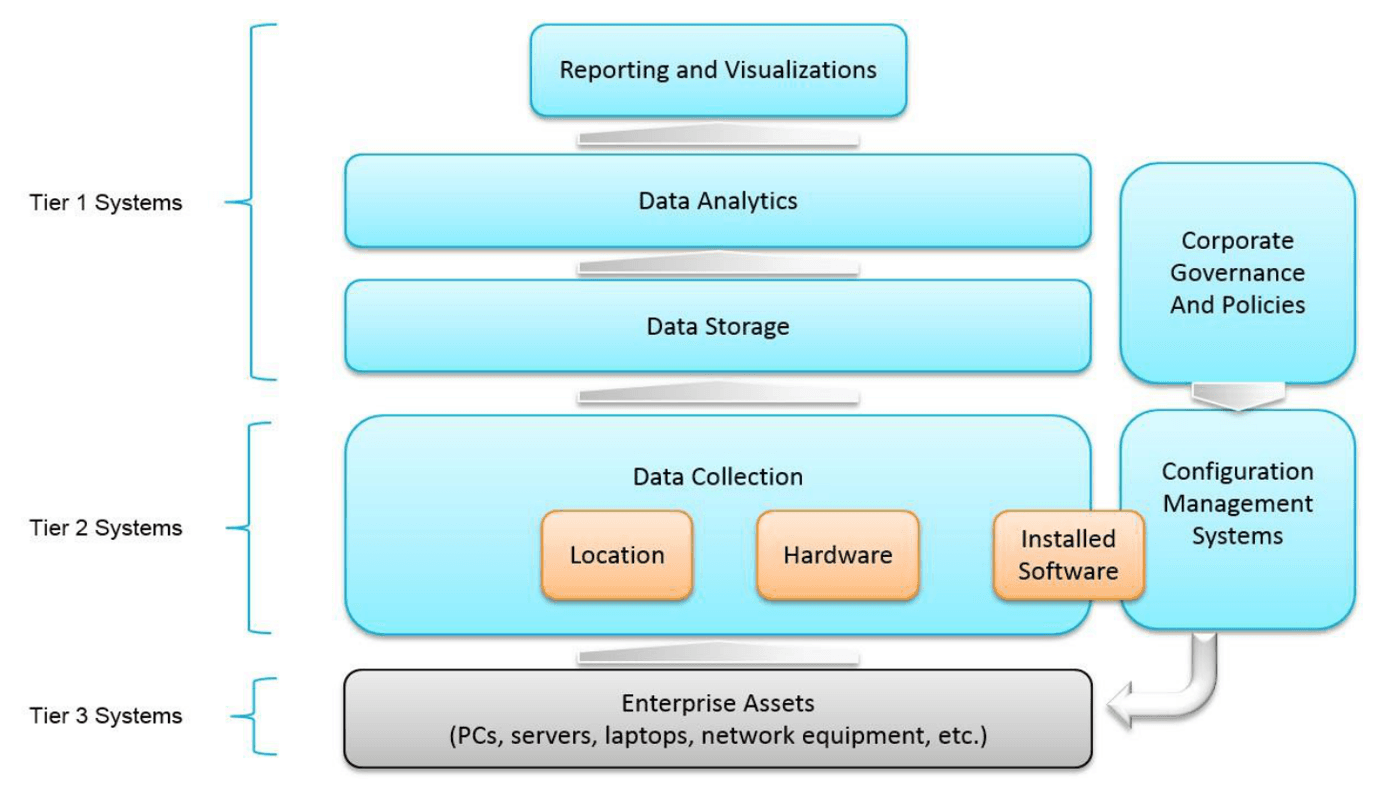
Collect from what already exists, such as device management tools, cloud consoles, and finance and purchasing records for SaaS. Compare the result with a network scan.
Assign owners. To keep the list current, tie it to purchasing, onboarding and change processes, and review it on a set rhythm.
A worked case
An architecture firm with 30 staff counts 34 laptops, 2 servers and 19 SaaS services. Going through card payments, it finds six tools nobody had declared, one of them holding project files with personal data.
Each gets an owner and a criticality rating, and three are closed down.
Good practices
- Automate collection wherever you can, because manual lists go stale within weeks.
- Include cloud services and data along with the hardware.
- Record criticality, which guides both patching and recovery.
- Reconcile against purchasing regularly.
Common mistakes
- Treating it as a one-time count, which is out of date by the following quarter.
- Listing only hardware, although much of the valuable data now sits in SaaS.
- Going into so much detail that nobody can keep it current.
- Leaving IT as the owner of every business application.
Questions
- What counts as an asset?
- Anything of value to the way the company handles information: data, applications, devices, services, and sometimes people and premises.
- Is an asset inventory mandatory for ISO 27001?
- Control 5.9 is in Annex A, so the Statement of Applicability must address it, and in practice it is rarely excluded.
- What is the difference between an asset inventory and a CMDB?
- A configuration management database also tracks relations and changes between IT components. It can serve as the inventory if someone really maintains it.
- How much detail is enough?
- Enough to decide and to act. Group similar low-risk items and detail critical systems individually.
- How is shadow IT found?
- By comparing expense and card records, identity provider logs and network traffic with the list of approved services.